In this article 11 sections
A customer can type one address and reach your website in seconds, but several systems cooperate to make that happen. The URL tells the browser what it wants, DNS helps locate a service, an IP address helps the network reach it and the web server supplies the response.
These are connected concepts, not interchangeable names for the same thing. Understanding their different jobs makes it easier to move hosting, configure a domain or explain a fault to a provider.
Start with the parts of an address
Consider https://shop.example.com/products/notebook?colour=blue. This is a documentation example, not a claim that a particular shop is available. Its structure illustrates what a browser reads before requesting a page.
| Part | In the example | Purpose |
|---|---|---|
| Scheme | https | Selects the protocol used to access the resource |
| Hostname | shop.example.com | Identifies the named service |
| Registered domain | example.com | The domain beneath which shop is a subdomain |
| Path | /products/notebook | Identifies a resource within the web service |
| Query | colour=blue | Provides parameters interpreted by the application |
The full URL is more specific than the domain. DNS does not look up the product path or the colour parameter. It deals with names and record types; the application handles the requested page and query.
What an IP address contributes
An IP address identifies a network destination in the relevant routing context. IPv4 addresses use familiar dotted numbers; IPv6 uses a different, longer format. A website may have one or several addresses, or sit behind a CDN or other service.
A domain is not permanently attached to one IP. DNS records can change when hosting moves. Several hostnames can also point towards the same address, while the web infrastructure uses the requested hostname to select the appropriate website.
This is why entering a server IP in the address bar does not necessarily show your site. The server may host many domains, require a hostname for routing, or present a certificate that is valid for a domain rather than the numeric address.
Step 1: the browser interprets the URL
The browser identifies the hostname and requested resource. It may already have an appropriate connection or cached information, so not every visit repeats every network step. Browser policies and the website's previous responses can also influence how it proceeds.
For the example above, the hostname is shop.example.com. Changing the path would normally request another resource at the same service; changing the hostname could require different DNS information and a different connection.
Step 2: DNS supplies name information
The device asks its configured DNS resolution system for the required records. A recursive resolver may answer from cache. If it needs fresh information, it follows the DNS delegation hierarchy to the relevant authoritative service.
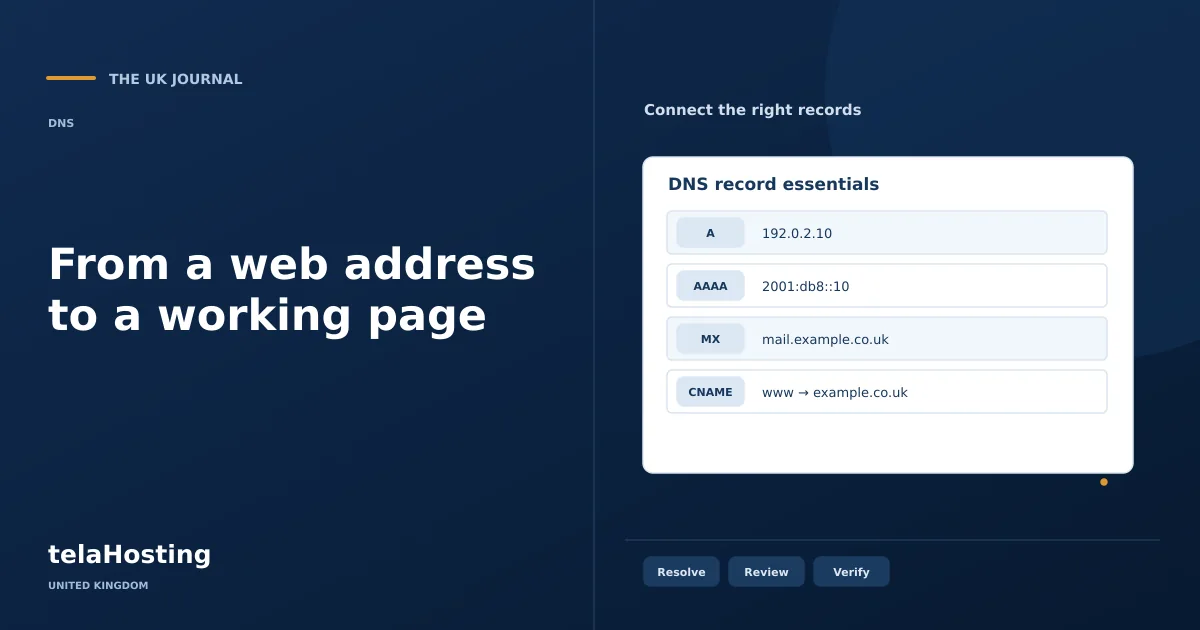
A records associate names with IPv4 addresses; AAAA records provide IPv6 addresses. A CNAME may direct the lookup to another hostname whose required address information is then resolved. Other record types serve jobs such as email routing or verification.
The authoritative data comes from the domain's active DNS provider, not automatically from its web host. Editing a zone at an inactive provider does not change the answer public resolvers receive.
Step 3: the device connects to the destination
With suitable address information, the browser can establish the network connection needed for the chosen web protocol. Modern deployments vary, but DNS's job at this stage is to provide the naming information rather than carry the page content itself.
Network routing, firewalls and the destination service must all permit the connection. A correct A record cannot repair an unavailable server or a firewall that blocks the required traffic.
Sites using IPv4 and IPv6 need both routes configured properly. A stale AAAA record can send some visitors to an old server even when a simple IPv4 check succeeds.
Step 4: HTTPS establishes a secure connection
For HTTPS, the connection uses TLS and the browser validates the site's certificate for the hostname. This helps protect the communication and establish that the service presents credentials appropriate to that name.
DNSSEC and HTTPS do different jobs. DNSSEC validates signed DNS data; HTTPS protects the web connection. Enabling one does not automatically configure the other, and a domain extension does not provide either by itself.
If DNS now points to a new host but the certificate is missing or covers the wrong hostname, visitors can see a warning. Fix certificate and host configuration at the destination rather than repeatedly replacing a correct DNS record.
Step 5: the server handles the requested resource
The browser sends an HTTP request for the path and any applicable query. The web server or application decides which content to return. It may retrieve files, query a database, authenticate a user or generate a response dynamically.
The response includes a status code and content or other instructions. A redirect tells the browser to request another URL. A 404 indicates that the resource was not found at the service; that is different from the hostname failing to resolve.
A CNAME does not replace this redirect mechanism. If a business wants /old-product/ to lead to /new-product/, it needs an appropriate HTTP redirect or application rule, not a DNS entry containing a page path.
Step 6: the browser loads page resources
The page can reference images, stylesheets, scripts and fonts. Some may use the same hostname and an existing connection; others may require requests to different services. A page therefore can partly load while a separate asset hostname fails.
When a design looks broken after a migration, inspect the failed resources. The cause might be an old application URL, a missing file, a security policy or another hostname's DNS configuration rather than the main domain itself.
Why www can behave differently
The main domain and www are separate DNS names. A website may redirect one to the other, but the initial name still needs to resolve and reach a service capable of handling the request. Configure certificate coverage for the names users will visit. A working homepage on one address therefore does not prove that both versions are connected correctly.
Use the layers to troubleshoot
| Observation | Likely area to investigate first |
|---|---|
| The hostname does not resolve | Delegation, DNS records, domain status or resolver |
| The address resolves but no connection completes | Network, firewall or destination service |
| The browser shows a certificate warning | TLS certificate and hostname configuration |
| The homepage works but a page returns 404 | Path, routing, application content or redirects |
| Only images or scripts fail | Asset URLs, files and their serving hostnames |
Collect the exact URL, time, error and network involved. Compare DNS answers with the intended provider settings. Then test the connection and application. This sequence prevents a page-path problem from triggering an unnecessary nameserver migration.
How the connection affects a hosting move
If your domain stays the same, you can prepare another hosting service and update the relevant website records. Preserve email and other dependencies. The destination must recognise the hostname, have the website data and support HTTPS before the move is complete.
If the domain or page URLs change, plan redirects and application updates as well as DNS. Keep a map of important old addresses and verify their new destinations. Moving a name alone does not move its content or preserve every external link.
A useful service inventory records the domain, authoritative DNS, website destination, certificate management and mail provider. Each layer has a separate role, and documenting those connections gives you a clearer path from a customer's URL to a working page.
Follow the subject
Your perspective
Join the discussion
Ask a question, share what worked, or add a useful detail.
Loading discussion…
Comment moderation
Only approved contributions appear in the discussion.